Govern Every Sensitive Data Exchange With a Data Control Plane
Patchwork point solutions — email, SFTP, MFT, web forms, file sharing, AI integrations — each typically managed by a separate tool with its own policies, logs, and security posture, exist in most organizations. Fragmentation is an unfortunate byproduct: an assortment of disconnected systems that create gaps attackers exploit, compliance officers can’t close, and IT teams can’t efficiently manage.
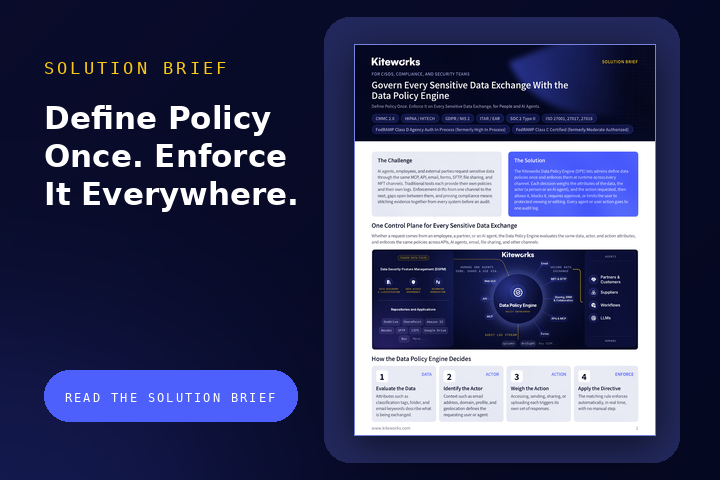
A data control plane solves the fragmentation problem, providing one policy engine, one audit log, and one security architecture across every workflow. With the Kiteworks Data Policy Engine, all sensitive data moving into, out of, or through your organization — whether accessed by an employee or an AI agent — now follows the ABAC and RBAC rules you set, automatically and consistently, across every workflow. The result? Full data control over the full data cycle.

End the Policy Silos That Create Compliance Gaps and Audit Failures
Most businesses have no unified way to govern sensitive data flows. Policies exist in silos: one tool for email, another for file transfer, another for collaboration, none of them coordinated. The result is inconsistent enforcement, compliance gaps, and audit nightmares that leave security and compliance teams reacting instead of governing.
Kiteworks closes these gaps with a single policy framework and unified audit log that governs every workflow under one consistent set of rules. Teams get one source of truth for enforcement and audit evidence, providing provable, consistent governance and the confidence that nothing is slipping through the cracks.
Unify Sensitive Data Governance Across Every Workflow With One Control Plane
Every modern enterprise manages an application layer, a network layer, and an infrastructure layer — each with a control plane that governs behavior at scale. But sensitive data has historically had no control plane of its own.
Kiteworks solves that problem with a single platform through which all sensitive data exchanges flow, governed by consistent policy, protected by enterprise-grade security, and captured in a unified audit log. Security, IT, and compliance teams now have one point of control and visibility across every workflow — so they can enforce policy consistently, close audit gaps, and govern sensitive data with the same certainty they expect from every other layer of the enterprise stack.

Enforce Data Governance Automatically Across Every Workflow With the Data Policy Engine
The Kiteworks Data Policy Engine draws on NIST Cybersecurity Framework principles to evaluate every sensitive data exchange across three factors simultaneously: what data is involved, who or what agent is taking the action, and what they are trying to do. That triangulation, known as attribute-based access control (ABAC), drives dynamic, real-time policy decisions for employees and AI agents alike, enforced automatically from a single control point.
The rule set maps directly to frameworks including CMMC 2.0, HIPAA, GDPR, FedRAMP, and ITAR, and requires no manual intervention to enforce. Every action is logged in a comprehensive, immutable audit log that feeds directly into compliance reporting and SIEM integrations.


Accelerate Policy Deployment With Pre-Built Templates and IF-THEN Rule Logic
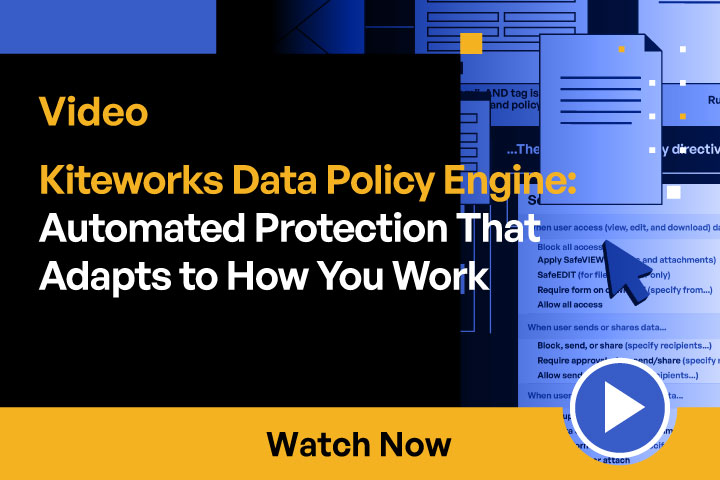
Define ABAC data policies as simple IF-THEN rules built from three elements: the data, the user or agent, and the action. The IF condition matches data attributes — folder paths, classification labels (MIP sensitivity labels or Kiteworks tags), or keywords in an email’s subject or body — together with user or agent attributes such as domain, identity, profile, or real-time geolocation.
The THEN directive sets the response based on the action. For data access: block, grant view-only access (SafeVIEW), possessionless editing (SafeEDIT), require a justification form, or allow full access. For sending or sharing: block, require manager approval, or allow. For uploads or attachments: block, apply a specific Kiteworks tag, require a justification form, or allow the action.
Respond to Every Data Movement Instantly With Real-Time Policy Enforcement
As data moves across any Kiteworks workflow, the data policy engine evaluates it in real time against your organization’s policy conditions — reading data attributes, identifying the actor (employee or AI agent), and determining the action requested. The matching directive fires automatically. No human intervention required. No workflow-specific gaps. No after-the-fact remediation that waste valuable time and resources. Instead, you get uniform enforcement across all workflows and all actor types. And compliance is built into the architecture, not bolted on.


Govern Every User and Every Asset With Granular Role-Based Access Controls
Kiteworks least-privilege role-based access (RBAC) roles define what each class of user can do, such as file types they can upload, whether they can send email and with what forwarding and expiration options, which clients and plugins they can use, and whether they can create folders or invite other users. Administrative duties are separated across distinct roles to enable compliant management of privileges.
At the folder level, granular access roles range from view-only through full management — with owners able to delegate day-to-day administration to managers. Time-based controls let administrators set expiration on user accounts, folders, files, and shared links, automatically revoking access when it is no longer needed.
Enforce Compliance Automatically and Prove It With a Comprehensive, Unified Audit Log
The Data Policy Engine makes compliance operational, not just documentable. Kiteworks enforces adherence in real time at the point of data movement. Policy controls map directly to specific regulatory requirements, automated enforcement eliminates human error and policy drift, and the unified audit log simplifies evidence collection for assessments and audits.Regulatory frameworks supported include:
- CMMC 2.0
- HIPAA / HITECH
- GDPR / NIS 2
- FedRAMP Class C Authorized and Class D Agency Auth In Process
- ITAR / EAR
- SOC 2 Type II
- ISO 27001, 27017, 27018


Get More Than Policy Enforcement With a Complete Secure Data Exchange Platform
Email, file sharing, MFT, SFTP, APIs, and data forms come together under one policy framework and audit log so employees and AI agents operate under the same rules — providing consistent control and eliminating the blind spots that come from managing workflows separately.
A CISO Dashboard turns scattered activity logs into real-time, drill-down visibility — who sent what, to whom, when, and where — and feed directly into your SIEM.
A hardened, single-tenant deployment option provides full control of your environment, delivering data isolation and peace of mind. For the most demanding compliance standards, FedRAMP Class C Authorized and Class D Agency Auth In Process deployments let you pursue government and regulated-industry business with confidence.
Frequently Asked Questions
Policy silos refer to the fragmented approach of having separate policies for different tools like email, file transfer, and collaboration without coordination. This leads to inconsistent enforcement, compliance gaps, and audit failures, leaving security and compliance teams in a reactive mode rather than a governing one.
The Kiteworks platform acts as a control plane for sensitive data, allowing all exchanges to flow through a single platform. It enforces consistent policy, provides enterprise-grade security, and maintains a unified audit log, ensuring comprehensive governance across every workflow.
The Data Policy Engine (DPE) is at the core of the Kiteworks platform, evaluating data movement in real time against policy conditions and enforcing directives automatically. It maps controls to regulatory requirements, eliminates human error, and simplifies evidence collection with a unified audit log for compliance assessments.
Beyond policy enforcement, Kiteworks provides a complete secure data exchange platform consolidating email, file sharing, MFT, SFTP, APIs, and data forms under one framework. It offers FedRAMP Certified, hardened single-tenant deployments, and a CISO Dashboard for real-time visibility and reporting on sensitive data activity.
Featured Resources
Kiteworks Data Policy Engine: Automated Protection That Adapts to How You Work